
Description
Publisher's Note: Products purchased from Third Party sellers are not guaranteed by the publisher for quality, authenticity, or access to any online entitlements included with the product.
The latest Web app attacks and countermeasures from world-renowned practitioners
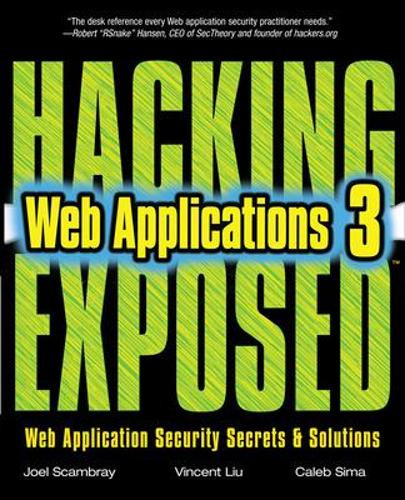
Protect your Web applications from malicious attacks by mastering the weapons and thought processes of today's hacker. Written by recognized security practitioners and thought leaders, Hacking Exposed Web Applications, Third Edition is fully updated to cover new infiltration methods and countermeasures. Find out how to reinforce authentication and authorization, plug holes in Firefox and IE, reinforce against injection attacks, and secure Web 2.0 features. Integrating security into the Web development lifecycle (SDL) and into the broader enterprise information security program is also covered in this comprehensive resource.
- Get full details on the hacker's footprinting, scanning, and profiling tools, including SHODAN, Maltego, and OWASP DirBuster
- See new exploits of popular platforms like Sun Java System Web Server and Oracle WebLogic in operation
- Understand how attackers defeat commonly used Web authentication technologies
- See how real-world session attacks leak sensitive data and how to fortify your applications
- Learn the most devastating methods used in today's hacks, including SQL injection, XSS, XSRF, phishing, and XML injection techniques
- Find and fix vulnerabilities in ASP.NET, PHP, and J2EE execution environments
- Safety deploy XML, social networking, cloud computing, and Web 2.0 services
- Defend against RIA, Ajax, UGC, and browser-based, client-side exploits
- Implement scalable threat modeling, code review, application scanning, fuzzing, and security testing procedures
About the Author
Joel Scambray, CISSP, is Managing Principal with Citigal as well as Co-Founder of Consciere LLC. He was previously chief strategy officer for Leviathan Security Group. He has assisted companies ranging from newly minted startups to members of the Fortune 50 in addressing information security challenges and opportunities for over a dozen years. Joel's background includes roles as an executive, technical consultant, and entrepreneur. He was a senior director at Microsoft Corporation, where he led Microsoft's online services security efforts for three years before joining the Windows platform and services division to focus on security technology architecture. Joel also co-founded security software and services startup Foundstone, Inc. He has also held positions as a Manager for Ernst & Young, Chief Strategy Officer for Leviathan, security columnist for Microsoft TechNet, Editor at Large for InfoWorld Magazine, and director of IT for a major commercial real estate firm. Joel has spoken widely on information security at forums including Black Hat, I-4, and The Asia Europe Meeting (ASEM), as well as organizations including CERT, CSI, ISSA, ISACA, SANS, private corporations, and government agencies such as the Korean Information Security Agency (KISA), FBI, and the RCMP. Joel Scambray is the co-author of all 6 editions of Hacking Exposed. He is also the lead author of Hacking Exposed Windows and Hacking Exposed Web Applications. McGraw-Hill authors represent the leading experts in their fields and are dedicated to improving the lives, careers, and interests of readers worldwide Caleb Sima is the co-founder and CTO of SPI Dynamics, a web application security products company, and has more than 12 years of security experience. His pioneering efforts and expertise in web security have helped define the direction the web application security industry has taken. Caleb is a frequent speaker and expert resource for the press on Internet attacks and has been featured in the Associated Press. He is also a contributing author to various magazines and online columns. Caleb is a member of ISSA and is one of the founding visionaries of the Application Vulnerability Description Language (AVDL) standard within OASIS, as well as a founding member of the Web Application Security Consortium (WASC).
Book Information
ISBN 9780071740647
Author Joel Scambray
Format Paperback
Page Count 482
Imprint Osborne/McGraw-Hill
Publisher McGraw-Hill Education - Europe
Weight(grams) 822g
Dimensions(mm) 229mm * 185mm * 24mm


